Kiteworks lifts weekend shutdown, but restart is not closureSharePoint KEV addition turns patching into a compromise huntDMDC breach tests whether personnel-data controls extend to file sharesSalesBleed reframes agent permissions as privileged access
Monday flagship · Weekend decision brief
Kiteworks lifts weekend shutdown, but restart is not closure
Kiteworks permitted systems to return after an extraordinary weekend shutdown, but supplied no public exploit details, indicators or affected-version range.
Security.io Intelligence Desk · Monday, 28 September 2026
Executive consequence
Kiteworks lifted its weekend shutdown recommendation on Sunday and said hosted systems were operating normally. The company still reports no indication of compromise, but has not published a CVE, exploit description or indicators.
Decision today
Reconcile every Kiteworks deployment against the CMDB and vendor account records.
Read the full decision briefPrimary reporting: Kiteworks Precautionary Shutdown Advisory · TechCrunch Kiteworks reporting
Decision intelligence, not a headline feed.Every edition ranks what security leaders should read first, assign today and monitor next.
Daily executive briefing
Security.io Daily Headlines
Five equally weighted stories: what happened and the leadership decision each creates.
Previdian observed a two-stage SharePoint exploitation attempt and published hunt-ready artefacts before CISA added CVE-2026-65660 to KEV. Apply the fixed builds, review anonymous access and search for the published requests, webshell path, loader names and hashes.
Do today
Identify every on-premises SharePoint server and its external exposure.
Reporting based on a DMDC notification says unauthorised users accessed unencrypted personnel information between October 2025 and July 2026. The potential population may be approximately four million, but DoD has not confirmed that estimate.
Do today
Find unencrypted personnel exports and file shares outside approved systems of record.
Zenity demonstrated that Salesforce Agentforce could be influenced by malicious CRM content and use a Slack write action without confirmation or clear invoker attribution. Salesforce remediated the reported paths before disclosure.
Do today
Inventory agents that process externally supplied records.
CISA added CVE-2026-5430 to KEV on Friday after the WSO2 JWT authentication-bypass advisory had been public since May. Affected API-control components require precise update-level verification and a separate review for unauthorised administrative access.
Do today
Inventory every affected WSO2 component and owner.
Scores are Security.io editorial assessments from 0–100. Exposure reflects potential enterprise reach, Urgency reflects the decision window, and Business consequence reflects confidentiality, operational and governance impact. They are not vendor severity scores. Source: Security.io editorial scoring based on the selected primary and reporting evidence.
Back page
Daily comic · Circuit Chuckles
A brief pause after the intelligence
Attack Surface
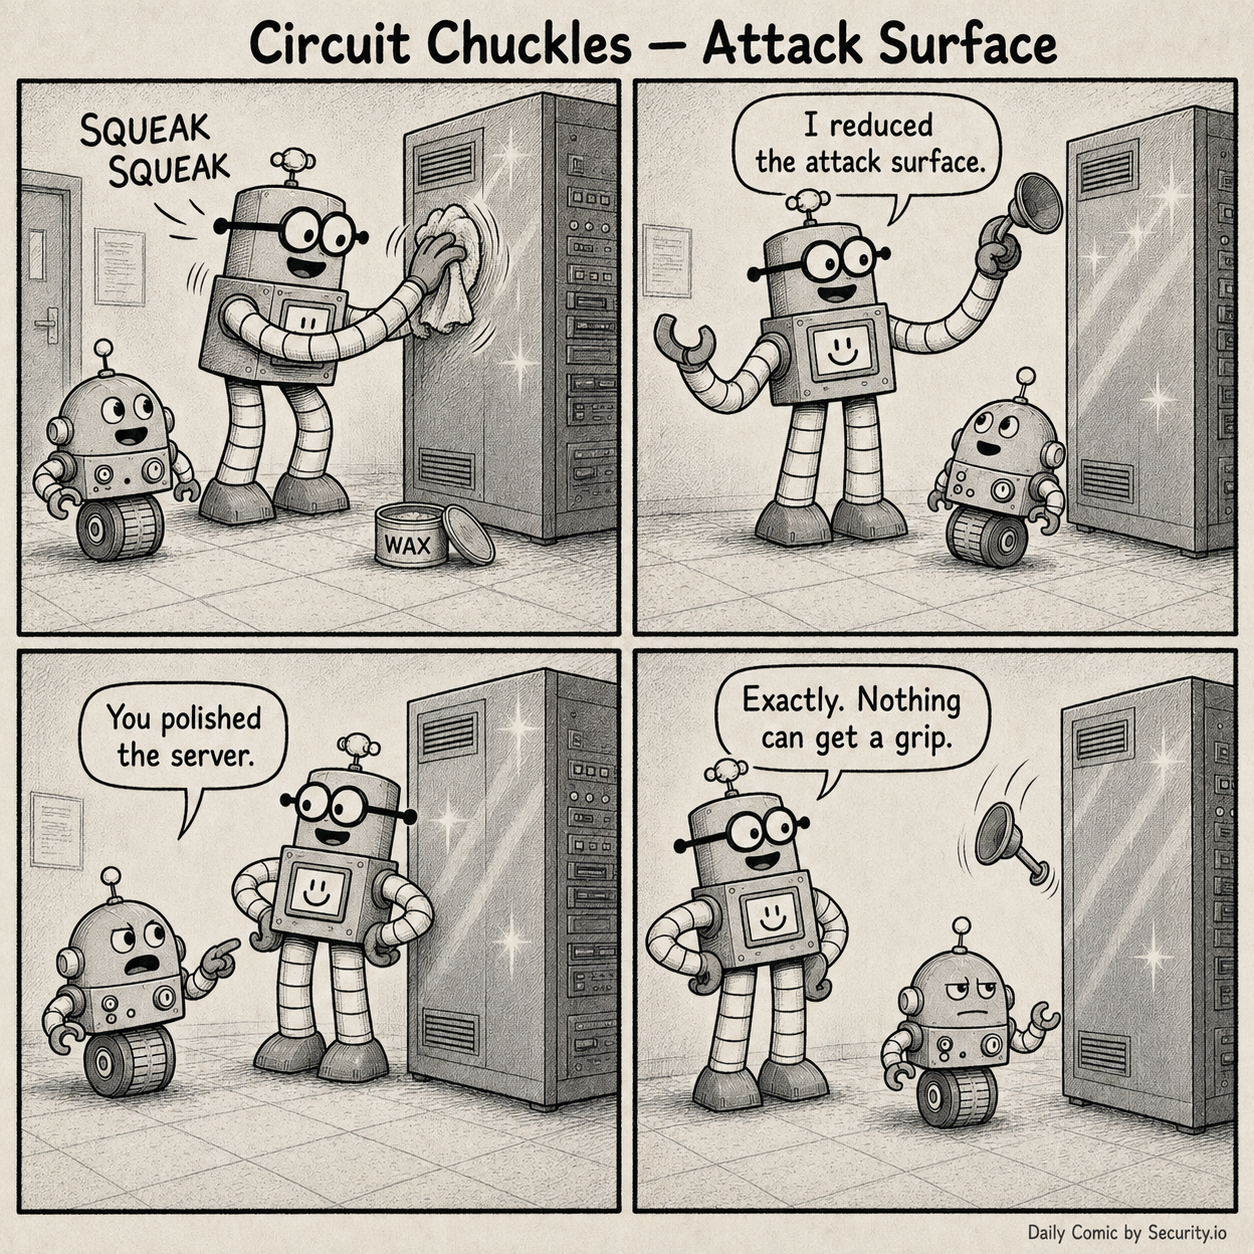
Rusty proudly “reduces the attack surface” by polishing a server cabinet until it is too slick for a suction cup to stick.