FortiMail zero-day reaches Monday as a compromise investigationCIRCIA final rule enters White House reviewPantheon widens affected-site count in platform-host incidentWarlock keeps turning SharePoint debt into critical-sector ransomware
Monday flagship · Weekend decision brief
FortiMail zero-day reaches Monday as a compromise investigation
Active exploitation, a passed federal remediation deadline and unavailable fixed builds make FortiMail a forensic investigation, not simply a Monday patch task.
Security.io Intelligence Desk · Monday, 5 October 2026
Executive consequence
Fortinet disclosed active exploitation of CVE-2026-104286 in FortiMail and published file, hash, IP-address and log indicators. CISA placed the flaw in its Known Exploited Vulnerabilities catalogue with an October 4 federal deadline and a forensic-triage requirement.
Decision today
Inventory every self-managed and provider-managed FortiMail instance; record version, exposure, IBE status and accountable owner.
The Office of Information and Regulatory Affairs recorded receipt of CISA’s CIRCIA reporting requirements at the final-rule stage. The submission is not the published rule and does not yet establish an effective compliance date.
Do today
Name legal, security and operational owners for CIRCIA applicability, clock initiation and submission authority.
Salt Labs disclosed a resolved proof-of-concept chain in which a malicious email influenced the Manus agentic AI platform and produced code execution inside its cloud sandbox before the warning could stop the action.
Do today
Inventory agents connected to email, cloud storage, repositories and administrative APIs.
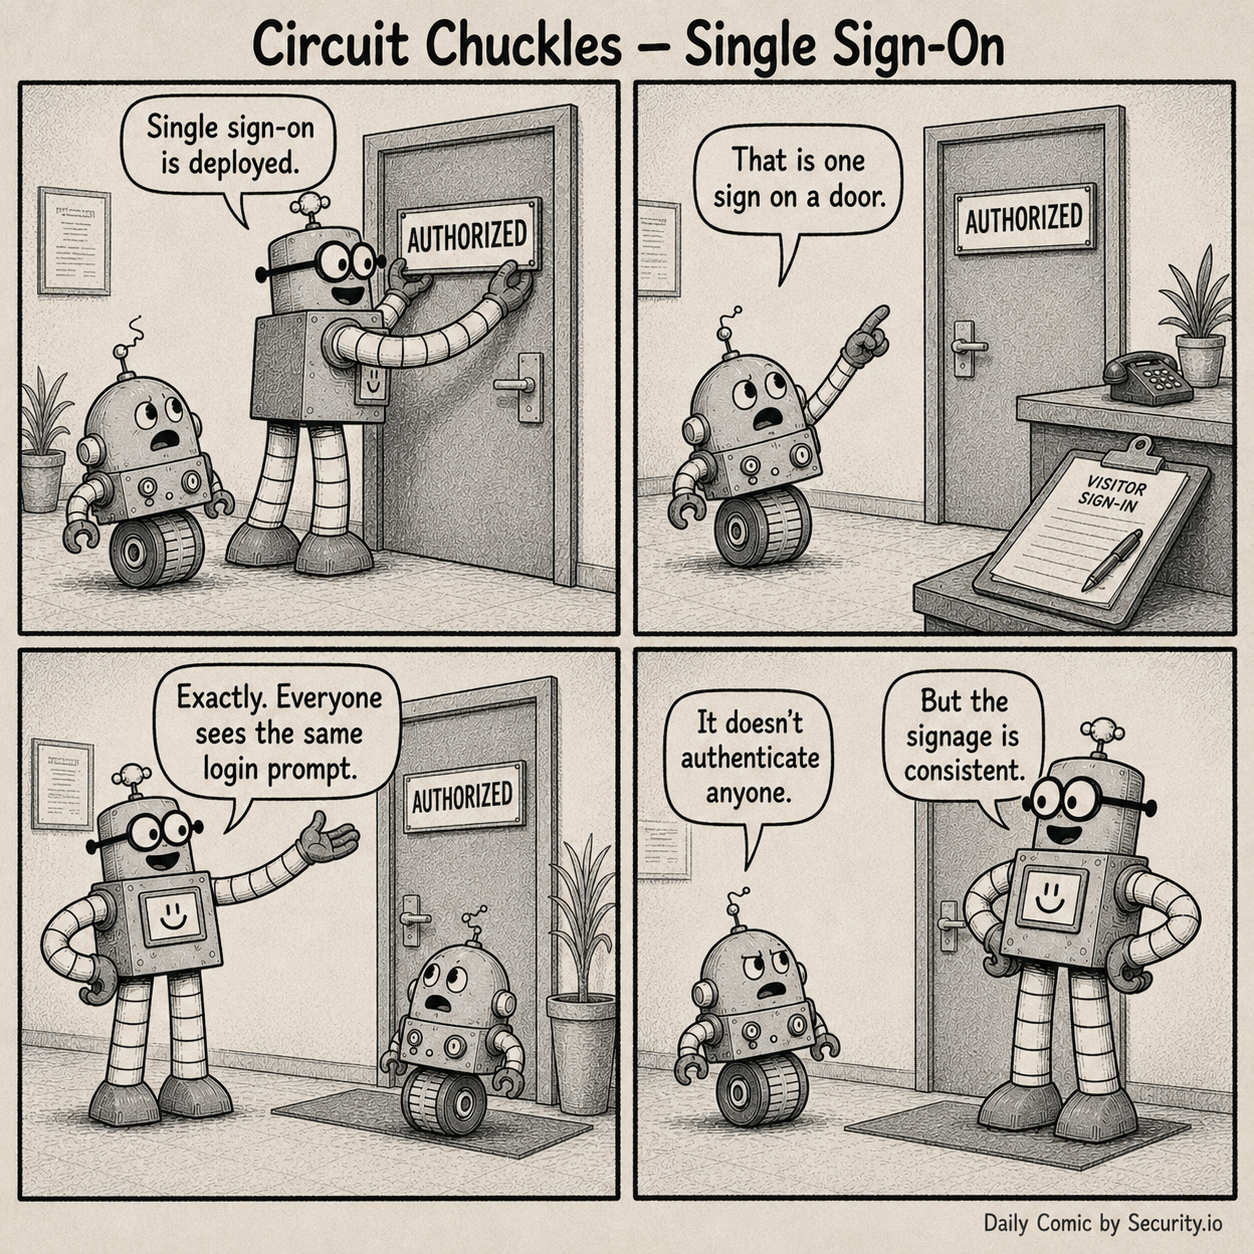
Rusty proudly deploys “single sign-on” by mounting one authorized sign on an office door, while Glitch points out that the system authenticates nobody.