VMware vCenter zero-day requires a compromise hunt, not patch-only…N-able email-security control plane stays offline after server intrusionEuropean Commission confirms AI-assisted campaign after application…UK tribunal confirms Apple received a technical capability notice
VMware vCenter zero-day requires a compromise hunt, not patch-only closure
A suspected PRC-linked espionage actor used the unauthenticated vCenter flaw before disclosure to create privileged SSO access, steal signing material and pivot into ESXi infrastructure.
Security.io Intelligence Desk · Friday, 20 November 2026
Executive consequence
Broadcom has fixed CVE-2026-123890, a critical unauthenticated VMware vCenter authentication bypass. Mandiant says ARMORY CASTLE exploited it as a zero-day, using specialised tooling to obtain vCenter identity material, create administrative access and move into ESXi infrastructure.
Decision today
Inventory every vCenter and VMware Cloud Foundation instance, including non-production and management-only networks.
Read the full decision briefPrimary reporting: Broadcom VMSA-2026-0009 advisory · Google Threat Intelligence Group and Mandiant · SecurityWeek
Decision intelligence, not a headline feed.Every edition ranks what security leaders should read first, assign today and monitor next.
Daily executive briefing
Security.io Daily Headlines
Five equally weighted stories: what happened and the leadership decision each creates.
N-able has reclassified a multi-day Mail Assure and SpamExperts Hosted Cloud disruption as a security incident involving unauthorised access to a server. Mail filtering continues, but management, API, quarantine, logging and mailbox-synchronisation functions remain offline.
Do today
Map every Mail Assure and SpamExperts tenant, API integration, OAuth grant and local administrator.
The European Commission has confirmed an AI-assisted cyber campaign detected on 22 October and initially confirmed on 26 October. Several applications were taken offline as a protective measure, most were restored, and investigators had not found evidence of a breach affecting staff as a whole.
Do today
Review internet-exposed assets for reachable administrative panels and unnecessary services.
The UK Investigatory Powers Tribunal has confirmed that the Secretary of State gave Apple a technical capability notice under section 253 of the Investigatory Powers Act 2016.
Do today
Identify UK business data stored in iCloud and its required encryption assurance.
PHP released critical security updates on November 19 across maintained runtime branches. Enterprise application owners should identify affected services, assess deployment-specific exposure and verify applicable security fixes in production.
Do today
Inventory deployed PHP runtimes and their effective configurations.
Scores are Security.io editorial judgments from 0 to 100, not external measurements. Exposure reflects deployment breadth and privilege; Urgency reflects confirmed exploitation and the remediation window; Business consequence reflects control-plane, identity and downstream workload impact. Source: Security.io editorial scoring based on the Broadcom advisory and Mandiant incident evidence..
Back page
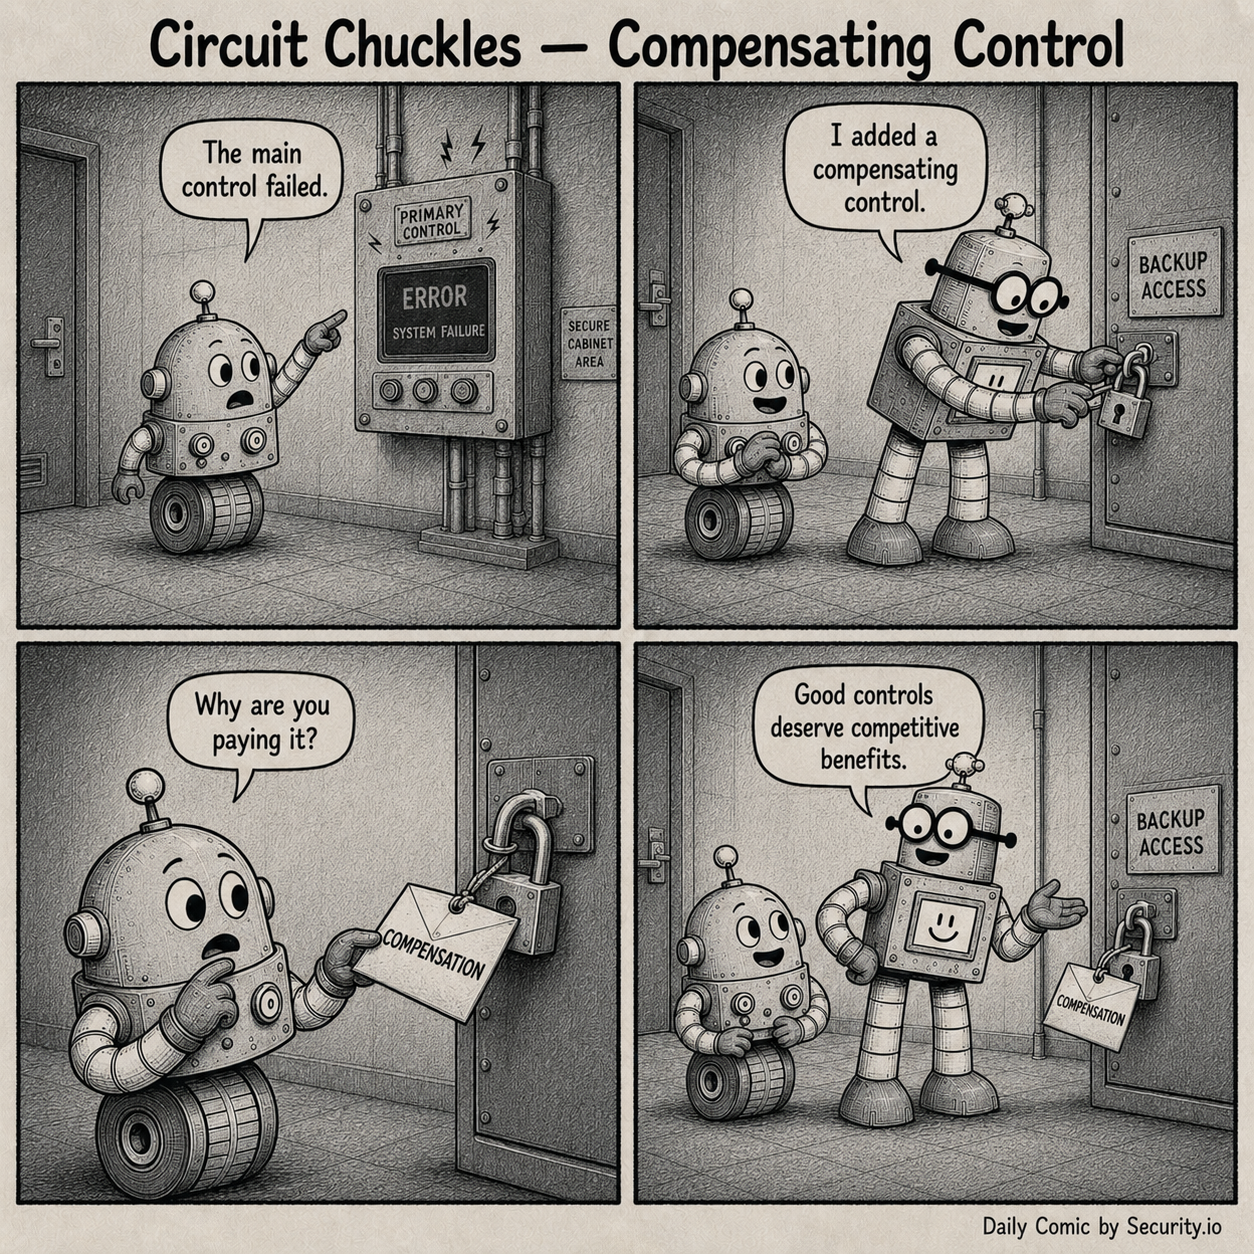
Daily comic · Circuit Chuckles
A brief pause after the intelligence
Compensating Control
Rusty mistakes a compensating control for literally compensating a backup control with benefits.